What Counts as a Deep Web Hack
A deep web hack is not a single attack type but a category of exploits designed to compromise users or services on the Tor network. Common targets include Tor Browser vulnerabilities, phishing clones of legitimate onion sites, malicious exit nodes that intercept traffic, and zero-day exploits in the Tor daemon itself. Attackers may also compromise darknet marketplaces to steal user credentials, cryptocurrency, or personal information stored in vendor and buyer accounts.
The distinction matters because deep web hacks often combine multiple techniques. An attacker might create a fake mirror of a popular marketplace, use social engineering to trick users into visiting it, and then deploy malware or capture login credentials. The anonymity that Tor provides also means victims often have no recourse and no way to report the theft to a conventional authority.
Common Attack Vectors on Tor
Phishing remains the most effective attack on the deep web. An attacker registers a similar onion address or creates a visually identical clone of a marketplace or forum, then advertises it on Reddit, Telegram, or other platforms where potential victims congregate. Users who log in with their credentials hand over their accounts directly.
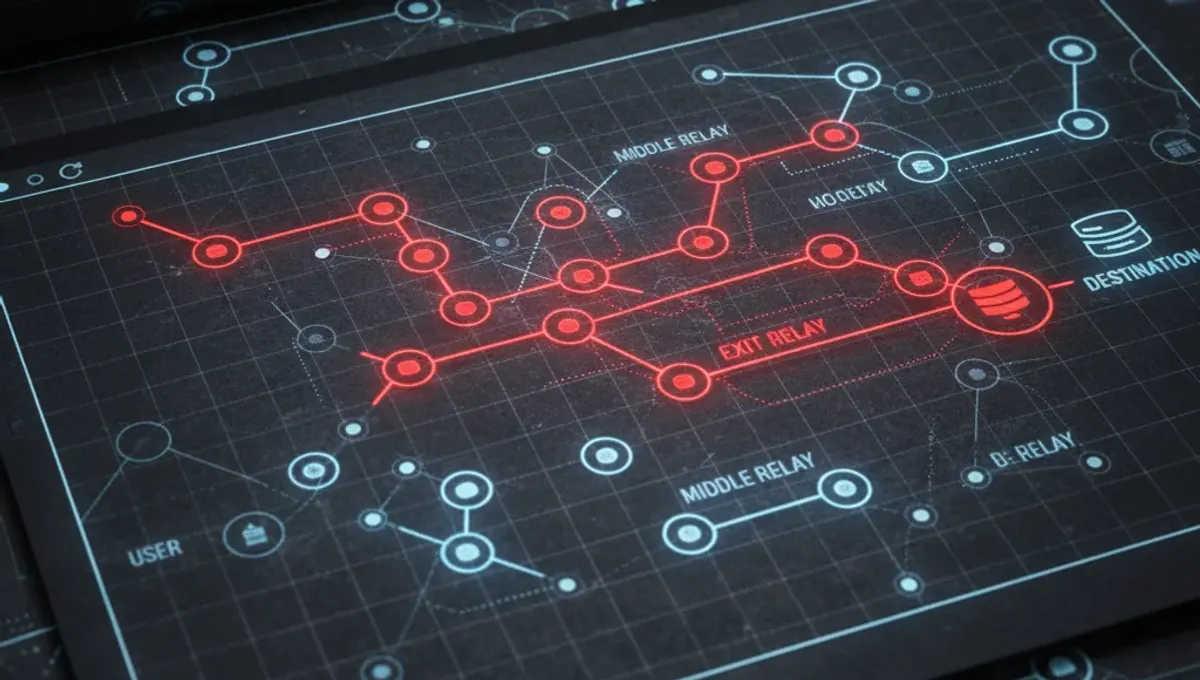
Malicious exit nodes represent another vector. A user connects to Tor, their traffic exits through a compromised node, and the attacker intercepts unencrypted data. This is why using HTTPS even on onion sites is critical, and why best deep web security practice involves never trusting exit nodes with sensitive information.
Browser exploits target Tor Browser itself. If a vulnerability exists in Firefox (the underlying engine), an attacker can craft a malicious webpage that, when visited, executes code and reveals the user's real IP address. These exploits are rare but devastating when they occur.
Marketplace Breaches and Exit Scams
Darknet marketplaces are frequent targets because they hold user funds, vendor credentials, and transaction histories. A breach can expose buyer and seller identities, cryptocurrency addresses, and shipping information. Some of the largest marketplace compromises have resulted in the theft of millions of dollars in cryptocurrency and the exposure of thousands of user accounts.
Exit scams occur when marketplace administrators simply disappear with user funds. This is not technically a hack but achieves the same result: users lose money and have no recourse. The best deep web market operators have historically used escrow systems and multisignature wallets to reduce this risk, but no system is foolproof. Users who store large amounts on any marketplace are taking a significant risk.
Reality Layer: How the Ecosystem Actually Fails
According to Tor Project documentation, the most common compromise vector is user behavior, not technical vulnerability. Users reuse passwords, click phishing links, and fail to verify onion addresses using PGP signatures. This matters because it means the best defense is operational security, not just software updates.
Public law-enforcement press releases on darknet marketplace seizures reveal that many breaches result from poor operational security by administrators themselves, not sophisticated hacking. Vendors and marketplace operators often use the same usernames across multiple platforms, making them vulnerable to de-anonymization through correlation attacks. Court records from prosecutions show that even experienced operators eventually make mistakes that lead to identification.
Security-vendor incident reports document that malware distribution on the deep web often relies on social engineering rather than zero-day exploits. Users download what they believe is a hacking tool or cracked software, only to find their system compromised. This pattern suggests that the deep web is not uniquely vulnerable to technical attacks but rather attracts users who are more willing to take risks with untrusted software.
How to Verify Onion Addresses and Avoid Clones
The most reliable way to verify an onion address is through a PGP-signed announcement from the site operator. Legitimate marketplaces and forums publish their official .onion address on multiple channels, signed with a private key that users can verify independently. If you have never seen a PGP signature before, this is the time to learn.
Steps to verify an address safely:
- Find the official PGP public key from the operator's website or a trusted archive.
- Obtain the signed announcement of the onion address from at least two independent sources.
- Use a PGP tool to verify that the signature matches the public key.
- Only then visit the address in Tor Browser.
Phishing clones often use addresses that are visually similar to the real one but differ by one or two characters. Always bookmark the verified address and access it only through your bookmark, never through search results or links from other users. The best deep web search engines like Ahmia and Torch index many mirrors, some of which may be malicious.
Protecting Yourself from Deep Web Exploits
Start with Tor Browser itself. Keep it updated to the latest version, as each release patches known vulnerabilities. Do not modify Tor Browser settings or install extensions, as these can compromise anonymity and security.
Use a dedicated device or virtual machine for deep web activity if you handle sensitive information. This isolates any potential malware from the rest of your system. If that is not feasible, use Tails or Whonix, which are operating systems designed specifically for anonymity and leave no persistent traces on your hardware.
Never maximize your browser window, as this can reveal your screen resolution and help an attacker fingerprint your system. Disable JavaScript in Tor Browser settings if you do not need it, as some exploits rely on JavaScript execution. Use HTTPS on every onion site, even if the site does not enforce it. Enable your browser's security warnings and never ignore them.
What to Do If You Suspect You Have Been Hacked
If you believe your deep web account has been compromised, change your password immediately from a different device and network. If you stored cryptocurrency on the compromised platform, move it to a wallet you control offline as soon as possible.
Document what happened and check whether your email address or personal information appears in public breach databases. Sites like Have I Been Pwned allow you to search for your email across known leaks. If your information is exposed, monitor your credit reports and consider placing a fraud alert with credit bureaus.
Report the incident to the platform operator if they have a security contact. Many legitimate marketplaces and forums have abuse or security email addresses. If the compromise involved financial loss, you may also report it to law enforcement, though recovery is unlikely. The key action is to prevent the same credentials from being used elsewhere and to isolate any malware on your system.
Moving Forward: Operational Security as Your First Defense
The reality of deep web security is that no technology can protect you from your own mistakes. The most sophisticated Tor setup fails if you reuse passwords, trust unverified links, or download untrusted software. Treat every interaction on the deep web as potentially hostile until proven otherwise.
Start today by choosing one practice to implement: either set up a password manager to generate unique passwords for each site, or learn to verify PGP signatures using a tool like Kleopatra or GPG Suite. These two habits alone will eliminate the majority of attack vectors you face. The best deep web links and top deep web resources all emphasize the same principle: your behavior matters more than the technology.
Common Questions
Can my IP address be revealed if I use Tor
Your IP address can be revealed only if a vulnerability exists in Tor Browser or the Tor daemon itself, or if you accidentally disable Tor while browsing. Malicious exit nodes cannot reveal your IP because they see only encrypted traffic if you use HTTPS. The safest practice is to keep Tor Browser updated and to assume your exit node is hostile.
What is the difference between a phishing clone and the real onion site
A phishing clone is a fake copy of a legitimate site designed to steal your credentials. The real site is verified through PGP-signed announcements from the operator. Clones often use addresses that look similar but differ by one character. Always verify the address through an official PGP signature before logging in.
Is it safe to buy things on darknet marketplaces
Darknet marketplaces carry significant risks including theft by vendors, marketplace breaches, law-enforcement seizure, and malware distribution. Even if a transaction completes, you have no legal recourse if the product is counterfeit or never arrives. Many users have lost money to exit scams and hacks.
How do I know if my deep web account has been hacked
Signs include unauthorized login activity, missing funds, changed passwords you did not change, or your information appearing in a public breach database. Check Have I Been Pwned to see if your email is in known leaks. If you suspect a compromise, change your password immediately and move any stored cryptocurrency to a wallet you control.
What is the best way to stay anonymous on the deep web
Use Tor Browser on an updated operating system, keep your browser window unmaximized, use HTTPS on every site, verify addresses through PGP signatures, and never reuse passwords. Consider using Tails or Whonix for sensitive activity. Operational security, not just technology, is what keeps you safe.